Manchester Airports Group Cyberattack: 8.7 Million Customer Records Exposed

 Ukraine's young figure skaters twizzle on despite Russian threat
 Asian football endorses Infantino re-election as FIFA president
 Complete Kane hopes for 'special night' as Ballon d'Or rumours swirl
 Rooney calls United squad 'selfish babies' after Fernandes criticism
 Teddy Wilson, son of World Cup-winner David, gets Wallabies call-up
 New Zealand military chief resigns over 'inappropriate relationship'
 Man Utd's Carrick on borrowed time, free-scoring Brighton face Liverpool
 Asian stocks head into weekend on a low as tech extends losses
 'Generational rage': Young Europeans fight to be heard
 Lula, Bolsonaro to clash once more before Brazil vote
 Dressed to kill: Haircuts cap menacing look of Japan's yakuza
 Napa Valley's wineries feel Trump's tariff squeeze
 Venezuela protests demand return of Nobel winning leader Machado
 Marquez tops incident-packed opening practice for Australian MotoGP
 New York votes to ban Central Park horse carriages after decades of debate
 Australia face selection headaches after 'shambolic' South Africa defeat
 Around 150,000 rally in Belgrade as Serbia heads to pivotal poll
 Hamilton sets sights on racing in African grand prix
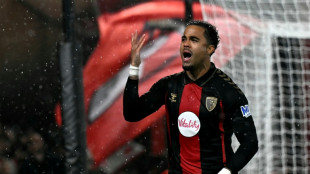 Bournemouth hammer 10-man Milan, Juventus denied at the death
 Judge orders Trump to give deposition in BBC lawsuit by Dec 11
 'Fake' pollsters hit US midterms
 Global markets retreat as tech mood sours, oil prices jump
 Juventus denied at the death, Sunderland make point in Poland in Europa League
 Tens of thousands rally as Serbia heads to pivotal poll
 Monet's 'Iris' fetches 50 mn euros at Paris auction
Manchester Airports Group (MAG) has confirmed that hackers accessed the personal data of up to 8.7 million customers during a significant cyberattack. The breach exposed email addresses, phone numbers, vehicle registrations, and postcodes collected through car park services, lounge bookings, and airport Wi-Fi sign-ups. While financial information remained secure, cybersecurity experts warn that the stolen data creates a heightened risk for sophisticated phishing scams targeting travelers during one of the UK's busiest travel periods.
Manchester Airports Group (MAG) has confirmed that a cyberattack resulted in the theft of personal data belonging to up to 8.7 million customers. The incident, which occurred as the UK approaches one of its busiest annual travel periods, compromised information gathered through various digital services operated by the airport group, which owns and manages Manchester Airport, London Stansted Airport, and East Midlands Airport.
The specific data accessed and stolen by the attackers includes email addresses, phone numbers, vehicle registration plates, and postcodes. According to MAG, this information was likely extracted from a large database linked to car park services, lounge access bookings, Fast Track security lane reservations, and in-airport Wi-Fi sign-ups. The scope of the breach suggests that hackers gained entry to a substantial repository of customer records rather than isolated accounts.
In a statement addressing the incident, MAG emphasized that immediate containment measures were enacted upon discovery. "We immediately contained the risk and have been working with specialist advisors and taking appropriate steps to protect our customers and systems," the company said. The organization confirmed it has informed relevant authorities and is cooperating with them. Crucially, MAG stated that at no point during the incident was passenger safety or aviation security compromised, and operational services at its terminals continued without disruption.
Despite the lack of operational interference, cybersecurity experts warn that the exposure of this specific dataset poses a severe threat to affected individuals. While banking details and financial information were not exposed, the combination of email addresses, phone numbers, vehicle registrations, and postcodes provides cybercriminals with enough personal context to craft highly convincing fraudulent communications.
Experts note that the stolen data can be weaponized to create targeted phishing and smishing campaigns. Because criminals possess legitimate travel-related details, such as customer number plates or specific service usage patterns, malicious messages are significantly harder for ordinary customers to distinguish from genuine correspondence. Potential scams could include fake parking refund notifications, alerts regarding Fast Track booking issues, or messages claiming to be official updates about the breach itself.
The vulnerability is particularly acute because a significant portion of MAG’s customer base includes frequent travelers and individuals using premium services. The majority of lounge and Fast Track bookings are made by wealthier passengers whose travel data may constitute sensitive or embarrassing information. This makes them attractive targets for unscrupulous cybercriminals who may use the data for blackmail, extortion, or sale to third parties.
Cybersecurity analysts have highlighted that the aviation sector has long been viewed as an attractive target for sustained cyber campaigns. The breach underscores the expanding attack surface of modern airports, where digital services such as Wi-Fi, parking apps, and booking systems have become integral parts of the security perimeter. When these connected systems are compromised, millions of people can be affected before they even board a plane.
"The absence of cancelled flights or queues at terminals does not make this a small cyber attack," one expert analysis noted. "Criminals know these people have a relationship with Manchester, Stansted or East Midlands airports and potentially have phone numbers, postcodes and vehicle registrations to make their approach believable. A fake parking refund, Fast Track problem or message about this very breach suddenly becomes much harder for an ordinary customer to spot."
MAG has advised affected customers to remain vigilant against suspicious emails and calls. The airport group warned that these communications could be highly specific, referencing flights, parking details, or airport services to appear legitimate. Customers are urged not to follow links in unexpected messages asking them to confirm information, make payments, or claim refunds. Instead, they should go directly to the airport’s official website to verify any claims.
For those who receive unsolicited calls claiming to be from the airport, MAG advises hanging up and contacting the organization independently through verified channels. Individuals who have already handed over banking information following suspicious contact are urged to speak to their banks immediately. Those who have disclosed passwords should change them on all platforms where they may have been reused and enable two-step verification.
The incident has prompted broader discussions about data minimization in the travel industry. Experts argue that companies must question not only how they protect customer data but also how much of it they need to collect and store in the first place. Reducing the volume of unnecessary data held by organizations can limit the potential damage caused when systems are breached.
Furthermore, analysts warn that the consequences of this breach may extend beyond immediate financial fraud. There is a risk that specialized cyber gangs could offer the stolen data to investigative journalists or other actors without disclosing its illicit origin. This could be used to track celebrities or trace sanction evasion, causing additional reputational and legal damage to victims.
In cases of extortion, many victims are unlikely to contact the police, opting instead to silently pay ransoms in cryptocurrency. However, such payments do not guarantee that the data will not eventually be released on the Dark Web or shared with third parties. Consequently, the breach is expected to have long-lasting consequences for the nearly 9 million affected individuals.
The incident serves as a stark reminder that maintaining operational continuity during a cyberattack does not equate to security success. While MAG has stated that operations were not disrupted, sensitive customer information was still accessed. Security experts emphasize that organizations must implement measures such as network segmentation to restrict access to critical systems and sensitive data, thereby reducing the risk that a single compromise leads to a wider incident.
As travelers prepare for peak holiday seasons, the erosion of trust caused by such breaches remains a significant concern. The exposure of personal data increases the likelihood of targeted attacks, requiring heightened vigilance from both consumers and industry operators. For travelers, the primary advice is to exercise extreme caution with any unexpected communication claiming to come from an airport, airline, or customer support team, and to avoid relying on public airport Wi-Fi for sensitive transactions.
C.Kreuzer--VB