Ireland fines LinkedIn 310 mn euros over EU data breach / Photo: © AFP/File

 Devan Ekambaram and Susha’s 'Varuvaaiy' Makes History as First Tamil Song Nominated for a Grammy
 Miranda Lambert Leads North Texans with Seven Grammy Nominations for 2027
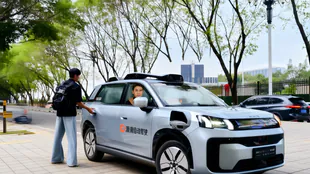 DiDi Advances Robotaxi Operations in China with New R2 Vehicle and Expanded Safety Infrastructure
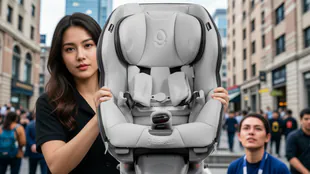 Smart Car Seats Tested: Do Sensors and Apps Actually Improve Safety?
An Irish regulator helping to police European Union data privacy said Thursday it had fined professional networking platform LinkedIn 310 million euros ($335 million) over breaching users’ personal data for targeted advertising.
The Data Protection Commission (DPC) issued the Microsoft-owned website its first EU fine saying "the consent obtained by LinkedIn was not given freely".
Targeted advertising is based on information held about an individual.
Regulators around the world, especially the EU, have been trying for years to regulate tech giants when it comes to data protection or unfair competition.
The DPC ordered LinkedIn to bring its processing into compliance with the EU’s strict General Data Protection Regulation, launched in 2018 to protect European consumers from personal data breaches.
"The processing of personal data without an appropriate legal basis is a clear and serious violation of a data subjects’ fundamental right to data protection," said Graham Doyle, the regulator's head of communications.
Ireland is home to the European headquarters of several tech giants including Microsoft, Apple, Google and Facebook-parent Meta.
The US Consumer Protection Agency (FTC) last year ordered Microsoft to pay $20 million to settle lawsuits for collecting personal data from minors registered on the Xbox console's online gaming platform, without informing their parents.
I.Stoeckli--VB